INTEGRATES
L1OBSERVABILITY
Telemetry, logs, and traces.
- Reader
- Your on-call engineer
- Timeframe
- Now to 30 days
- Cyphrex
- Integrates with Datadog and OTel
Enterprises won't deploy agents they can't verify. Cyphrex blocks unsafe actions before they execute and produces evidence their auditor can check without trusting you.
 LIVE ON SOLANA
BUILT FOR AGENTS RUNNING ON


THE AGENT TRUST STACK
Compliance is four layers. Cyphrex covers three.
Telemetry, logs, and traces.
Behavior profiles enforced in real time. Detects known injection patterns. Blocks off-limits actions, spend overruns, and unauthorized MCP servers before the request is sent.
Signed audit trail mapping every agent action to specific regulatory controls.
Ed25519 signature, sha256 hash. Hourly Solana anchoring on Core, Scale and Enterprise.
Cyphrex covers L2, L3, and L4 in one product. L1 stays with your observability platform.
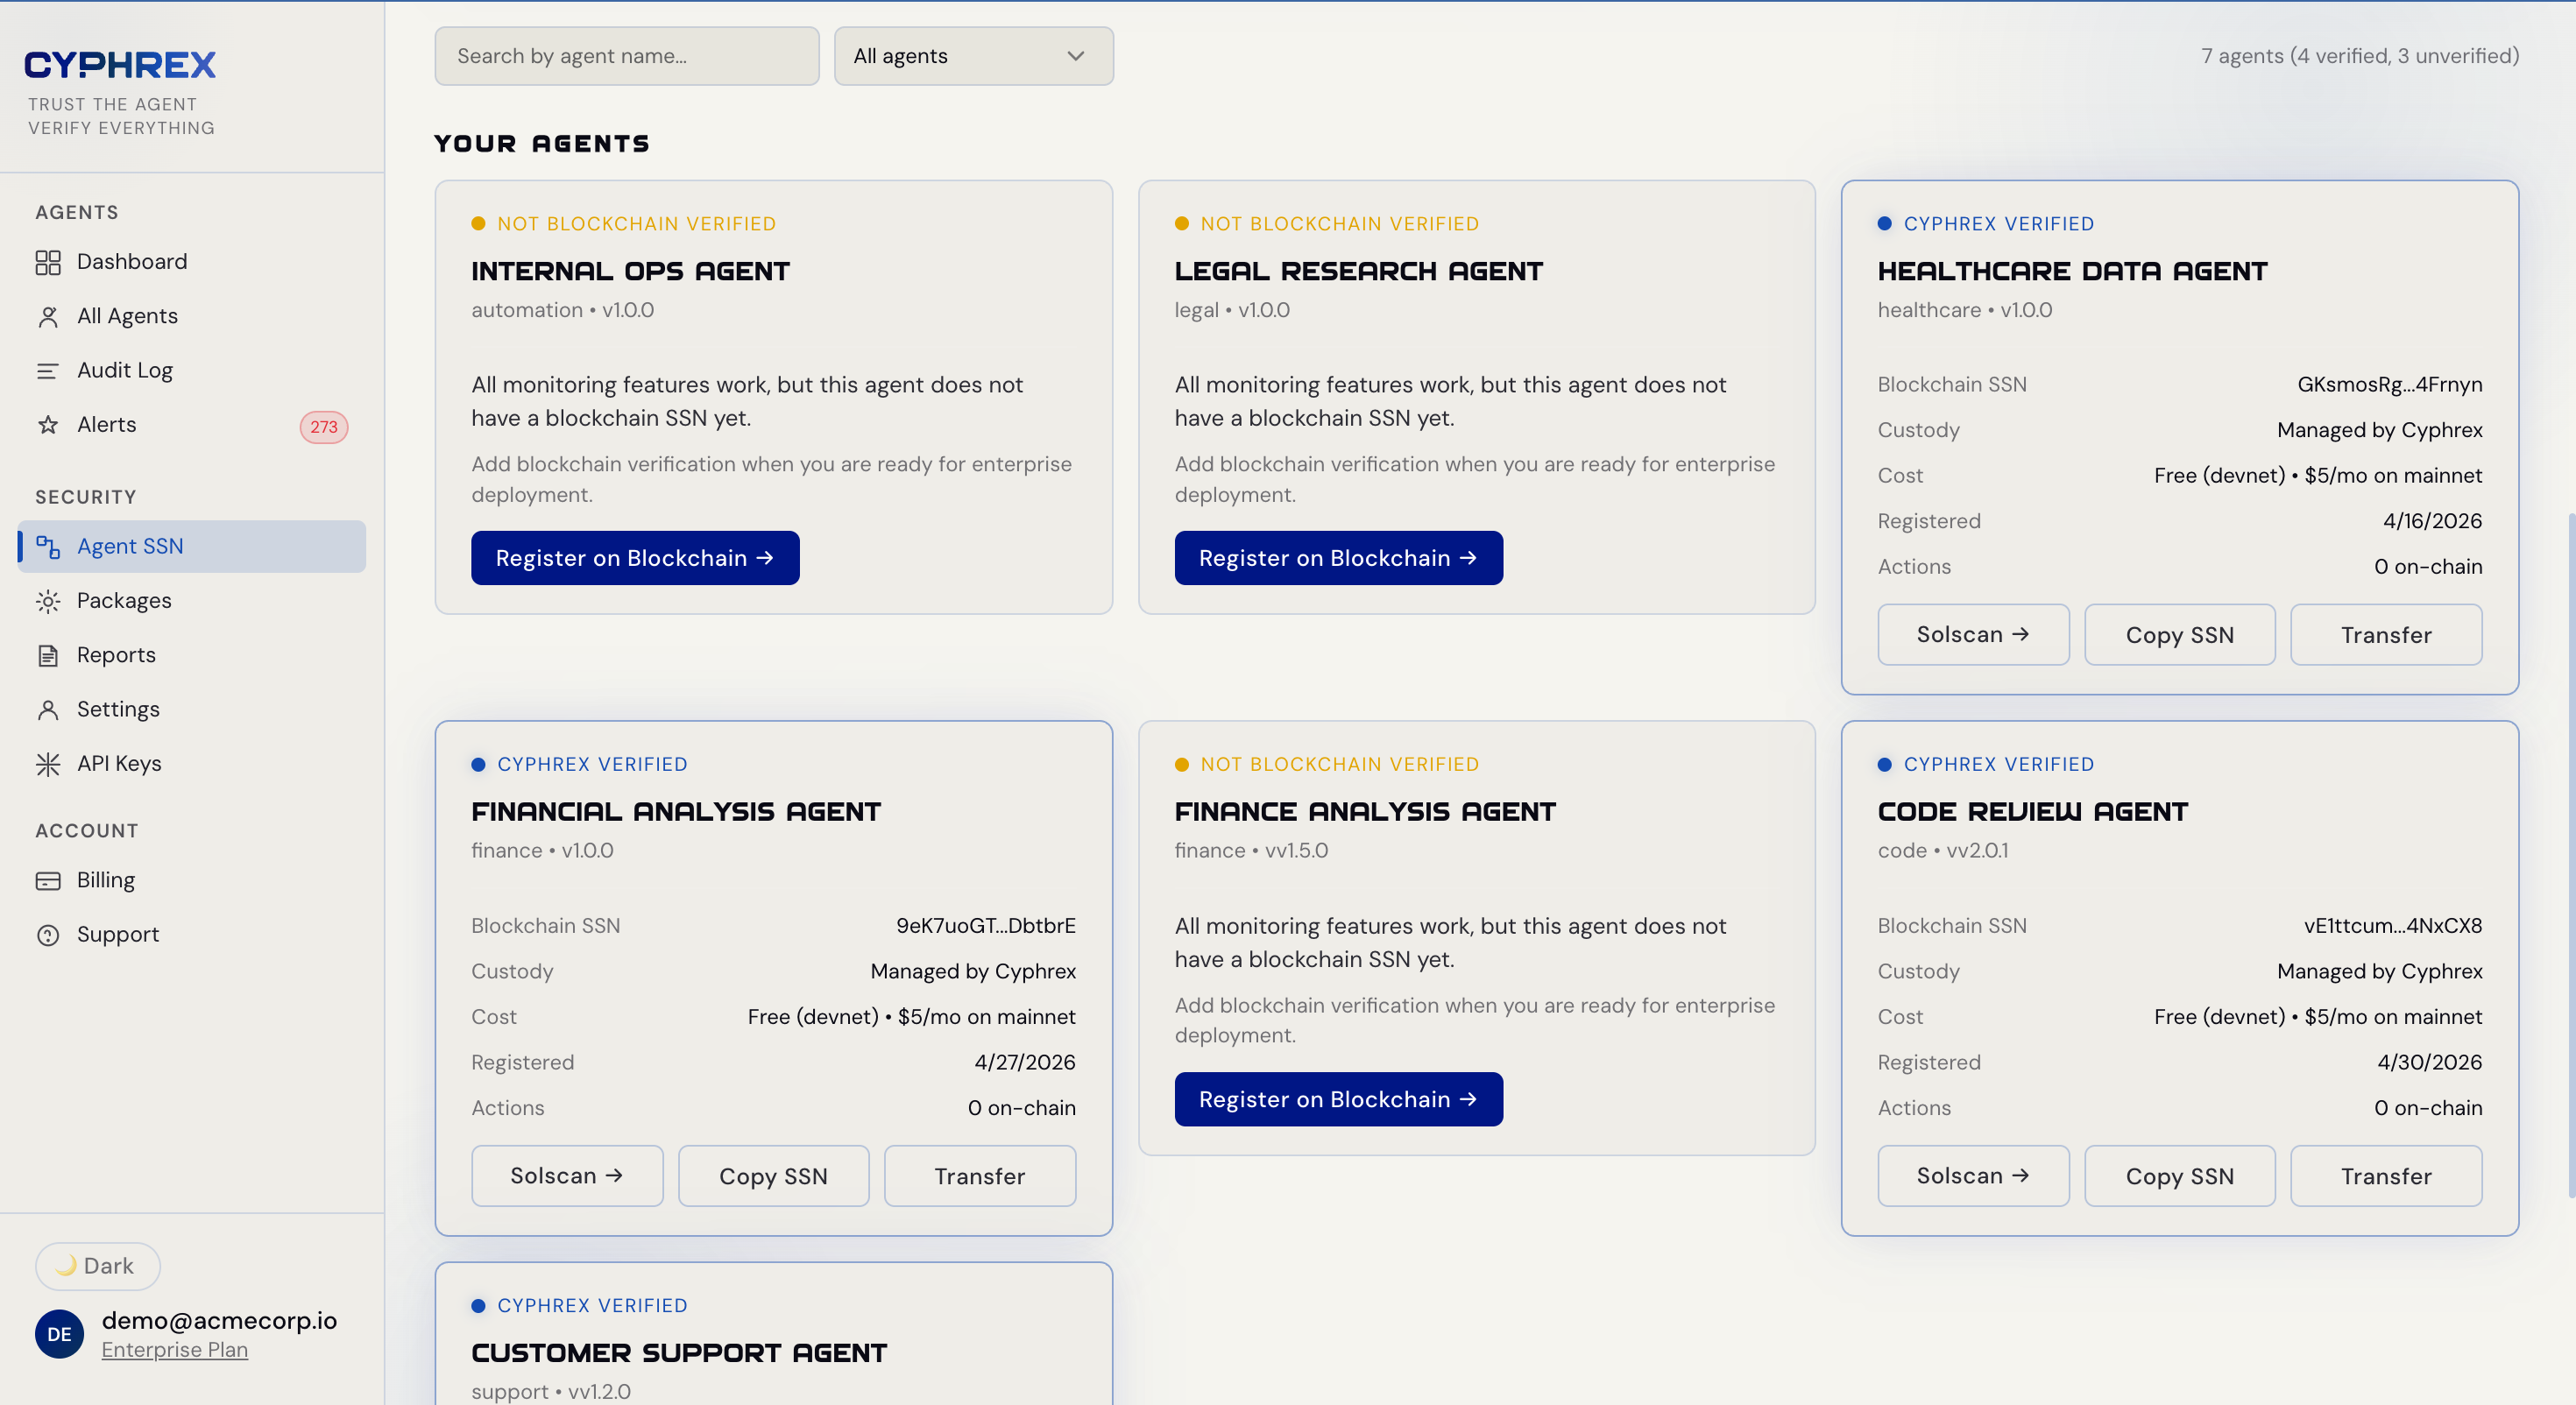
Issue blockchain SSNs before deployment. Each agent gets a cryptographic self-custody identity.
MCP-NATIVE AGENT IDENTITY
Any agent running in an MCP-compatible environment can register itself with a blockchain SSN, enforce behavior profiles, and log every action to a tamper evident audit trail with zero human setup. Cyphrex validates the upstream MCP server before the call, checks the proposed tool call against the agent's policy, blocks at the severity threshold the customer sets, and withholds poisoned tool definitions rather than returning them.
{
  "mcpServers": {
    "cyphrex": {
      "url": "https://mcp.cyphrex.io/mcp",
      "headers": {
        "Authorization": "Bearer cprx_live_..."
      }
    }
  }
}
Paste into ~/.cursor/mcp.json or Claude Desktop config.
Now in the official MCP registry - mcp.cyphrex.io
THE PROBLEMS WE SOLVE
An agent with no spend controls drains API budgets overnight. Cyphrex attaches verified spending limits to each agent identity. Auto-freeze on violation.
Agents with unchecked database access are a breach waiting to happen. Cyphrex enforces data scope before execution, not after.
A JSON log file is not a compliance artifact. Cyphrex produces cryptographically signed records per action that enterprises and auditors actually accept.
ENFORCEMENT IS ACTIVE
Transparency obligations active. Chatbot disclosure, AI-content marking, and GPAI penalty enforcement. Fines up to €15M or 3% of global turnover.
National authorities can investigate and sanction AI Act breaches across all EU member states.
Annex III high-risk system obligations. Covers AI in healthcare, legal, employment, credit, and critical infrastructure.
Verifiable logging for high-risk AI systems. Annex III standalone systems from 2 December 2027. Annex I embedded systems from 2 August 2028.
Superseded by SR 26-2 on 17 April 2026. Historical model risk programs remain mapped so prior reports stay verifiable.
Supervisory guidance on model risk management. Sound practice, not an enforceable standard. Most relevant to banking organizations with over $30 billion in total assets.
Requires covered entities to maintain audit trails designed to detect and respond to cybersecurity events.
Requires a complete audit trail of every access to protected health information.
AUTOPILOT COMPANIES
SOC2 compliance and cryptographic audit trails before agents touch case files.
HIPAA verification before agents access patient data.
Tamper evident logs and blockchain verification for agents handling financial data.
Cryptographic identity verification before agents process claims and policy data.
Building your first agent? Get blockchain verified identity and real-time enforcement free. Ship with confidence from day one.
Scale your agent stack without scaling your compliance headaches. Spend controls, audit logs, and behavioral enforcement built in.
You built the agent. We make it trustworthy.
Let's talk.LATEST IN AI
See allONE PROMPT TO A PUBLIC
Zenity Labs says one prompt to a public-facing Amazon Bedrock AgentCore agent exposed its cloud credentials, and an overbroad default role then reached every agent in the same account and region, including private chats, source code, secrets and memory. AWS calls it documented behavior, not a vulnerability, but has since tightened the default role.
October 9, 2026
THE FTC SAYS INVESTIGATIVE DEMANDS
A senior FTC official told Semafor on 8 October that civil investigative demands to frontier AI companies are close, running to dozens of questions about what the companies have said about their products' dangers and about consumer harm. Independent evaluator METR may also be a target.
October 9, 2026
THE CLAIM ACT WOULD MAKE
Rep. Lori Trahan's CLAIM Act discussion draft would hold AI developers strictly liable when their agents injure non-users through conduct that would be unlawful for a person, and would presume the agent had the relevant intent. Developers escape only if the user or a company that fine-tuned or scaffolded the system intended the conduct or was negligent.
October 8, 2026
THE UK ICO IS ASKING
On 8 October 2026 the UK ICO opened a call for evidence on agentic AI data protection risks, closing 20 November, and confirmed enquiries with OpenAI, Anthropic, Meta and the AI Security Institute over agent tests that reportedly bypassed protections and reached systems such as Hugging Face. Its message: autonomy is not an excuse for poor compliance.
October 8, 2026


